
Your AI-powered digital armor
Armadillo unifies security telemetry, deterministic detection, prevention and response, with an automated path from threat intelligence to deployable protection.

01Meet Armadillo01 / 07
Get to know Armadillo
A six minute walkthrough of the platform: deployment on a test server, a live attack detected and explained, and every module of the console.


02The challenge02 / 07
Attackers only need one way in.
Most organizations defend with a patchwork of tools. Every gap between them is a way in, and every minute an attack goes unseen it gets more expensive.
Too many tools, no single picture
Endpoint, network, identity and logs sit in separate products. An attack is split across screens, and nobody sees the whole story.
Alerts without explanations
Analysts face thousands of alerts with no reason attached. The real attack is buried in noise and false positives.
Protection that arrives too late
New threats and zero day exploits appear every day, while detection rules wait for the next vendor release.
Data that leaves your country
Many security products analyze your logs and traffic on servers abroad, and the detection logic stays with the vendor.
Armadillo was built to close these four gaps, in one platform. See the answer
03The answer03 / 07

Unified cyber defense.
One platform that sees your environment, understands what is happening in it, protects it with deterministic logic, and gives analysts the actions to respond.
-
01
See
Endpoint, network, process, file, session and port telemetry from enrolled agents and sensors.
-
02
Understand
Normalize, correlate and put security activity in context, with vulnerability and threat intelligence.
-
03
Protect
Deterministic detection rules, IDS evaluation and IPS enforcement, updated through versioned bundles.
-
04
Respond
Investigation, containment and response actions, every step recorded in an audit trail.
- ≤ 5 s
- maximum observed end to end time to protection, completed reported test set. Method
- Automatic
- from new intelligence to enforced protection, no manual rule writing
- Deterministic
- explicit, versioned, auditable detection logic
- Local
- analysis on site or on in country infrastructure
04How it works04 / 07
04.1The four steps
From installation to protection, in four steps
Every server follows the same path, from the first command to a recorded response. The sections that follow explain each step in detail.
- 01
Deploy
One command enrolls a server. The agent connects, starts monitoring and goes live with the full detection rule set.
Every host, in context - 02
Monitor
Processes, file changes, network traffic, sessions, ports and identities are recorded continuously on every server.
Network and sessions - 03
Detect and explain
Every detection becomes a clear alert: what happened, who attacked, what was targeted and why it fired. The AI engine updates rules automatically, in five seconds or less.
The protection engine - 04
Respond
Your team contains the threat with recommended, approved or automatic actions. Every step is recorded for audit.
Detection to action
04.2The protection engine
From new threat to active protection
New threat intelligence, or a sufficiently detailed attack description, goes in. Validated protection comes out, deployed and enforced in your environment automatically. No vendor release cycle, no manual rule writing.

New threat intelligence
Advisories, exploit information and indicators, or a detailed attack description.
Protection engine
Produces deterministic detection and prevention rules that are validated before release and remain auditable.
Internal method shared under NDAActive protection
A new versioned rule bundle, deployed to enrolled agents and engines and enforced where policy allows.
- Automaticfrom intelligence to enforcement
- Deterministicexplicit logic, not an opaque decision
- Validatedbefore any rule is released
- Auditableevery rule versioned and traceable
04.3Time to protection
Time to protection, measured end to end
≤5seconds
Maximum observed end to end time to protection across the completed reported Armadillo test set.
- Intelligence received
- Protection engine
- Bundle deployed
- Protection active
Replay of a documented benchmark. Stage positions show order, not individual durations.
05Capabilities05 / 07
05.1Endpoint visibility
Every host, in context
Every enrolled host reports agent health, rule bundle state, processes, file integrity and installed software, correlated with vulnerability intelligence. Select a host to investigate it.
Illustrative environment. Vulnerability mappings are real.

app-prod-04
Application server
- Operating system
- Linux, kernel 6.8
- IP address
- 10.20.2.14
- Agent
- Healthy
- Rule bundle
- Current
- Last seen
- 4 s ago
- IPS policy
- Enabled
- 1Open cases
- 1Exposures
- 2File changes, 24 h
- 1Flagged processes
| Process | PID | User | State |
|---|---|---|---|
| systemd | 1 | root | Normal |
| sshd (listener) | 812 | root | Normal |
| sshd: svc-deploy [priv] | 4402 | root | Normal |
| sshd: svc-deploy@pts/0 | 4405 | svc-deploy | Normal |
| bash | 4410 | svc-deploy | Normal |
| python3 /tmp/.x/upd.py | 4471 | svc-deploy | Suspicious |
| Time | Change | Path | SHA-256 | Severity |
|---|---|---|---|---|
| 10:42:41 | Createdby svc-deploy | /tmp/.x/upd.py | c41e…09ab | Medium |
| 10:43:20 | Modifiedby svc-deploy | /home/svc-deploy/.ssh/authorized_keys | 9f2c…a41e → 07bd…e913 | High |
Watched paths: /etc, /home/*/.ssh, /usr/bin
| Package | Version | Advisory | Severity |
|---|---|---|---|
| OpenSSH | 9.6p1 | CVE-2024-6387Signal handler race condition in sshd; fixed in 9.8p1 | High |
| Python | 3.10.12 | None known | Clear |
| OpenSSL | 3.0.13 | None known | Clear |
- 10:42:03Inbound SSH session accepted for svc-deploy from 203.0.113.45
- 10:42:41New file /tmp/.x/upd.py created
- 10:43:12python3 started from the interactive shell, PID 4471
- 10:43:15First seen outbound TLS connection to 198.51.100.7:443
- 10:43:20authorized_keys modified, a persistence indicator
- 10:43:21Signals correlated into case #2041, severity High
Awaiting analyst decision on case #2041.
05.2Network defense
Network defense, with policy you can see
Traffic is inspected, protocols identified and IDS rules evaluated. Prevention happens only where the IPS policy is enabled. Switch the policy to see the difference.

- Flow observed 198.51.100.23 to db, TCP 5432
- IDS rule matched AR-EXAMPLE-0142, severity high
- IPS enforced drop, block event recorded
- IPS disabled alert raised, traffic not prevented
- Correlated into case with host and session context
IDS path
- Event
- Rule evaluation
- Detection
- Severity
- Alert
- Correlation
IPS path Policy enabledPolicy disabled
- Detection
- Policy check
- Enforcement
- Block, drop or reject
- Audit event
Remote sessions
| Service | Initiator | Receiver | Direction | Duration | Confidence |
|---|---|---|---|---|---|
| SSH 22 | 10.0.4.21 | app-prod-04 | Inbound | 12 min | High |
| RDP 3389 | 198.51.100.23 | ws-fin-117 | Inbound | 3 min | Suspicious |
| FTP 21 | db-prod-02 | 203.0.113.9 | Outbound | 40 s | Medium |
Each session links to host events, alerts and cases.
Port exposure
- Baseline
- New port
- Classified
- Correlated
- Response path
- 443HTTPSBaseline
- 22SSHBaseline
- 3389RDPNewInternet exposedSuspicious serviceLinked to sessionBlock available
05.3Correlation
Fragmented telemetry becomes one investigation
Signals from different domains are normalized, deduplicated and correlated into a single case, with severity and workflow. Synthetic example.
- Ingest
- Normalize
- Correlate
- Deduplicate
- Severity
- Workflow
- Case
- Archive
- Report
- Notify
05.4Response
From detection to action
Armadillo does not stop at the alert. Prevention runs automatically where policy allows. Deeper actions are analyst initiated, authorized and audited. Select an action to follow its command path.
Automatic under policy
- Block, drop or rejectWhen the IPS policy is enabled, confirmed malicious traffic is prevented and logged
- Automatic IP blockingWhen auto blocking is enabled, detections queue a firewall block at the agent
- Protection updatesNew rule bundles are deployed to active environments automatically
Analyst initiated
Command lifecycle
Kill process python3, PID 4471 on app-prod-04 synthetic example
- Authorization
- Dispatch
- Agent check in
- Execution
- Status returned
- Audit
05.5Advanced modules
Beyond the endpoint. Ten advanced modules, one console.
Network behavior, identities, automated response, AI agents, sensitive data and global threat intelligence now sit beside endpoint detection, on the same data model and in the same console. Every screen below is the real product.
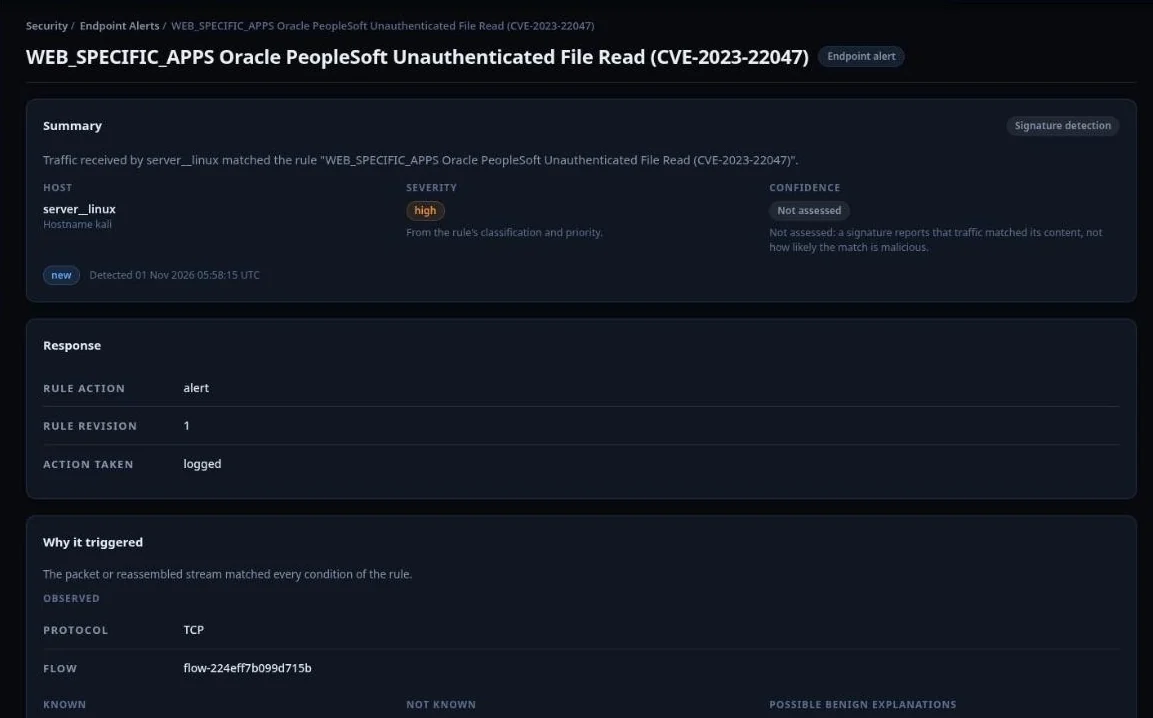
Every alert explains itself.
Open any alert and Armadillo shows why it fired: the rule that matched, the vulnerability it targets, the affected host, the attacker and the confidence. It also states what is known, what is not, possible benign explanations and the next steps to take.
- Threats named by vulnerability (CVE)
- Attacker and target on every alert
- What is known and what is not
- Possible benign explanations
- Recommended next steps
- Network context and evidence
OutcomeAnalysts understand every alert at a glance, without digging through logs.
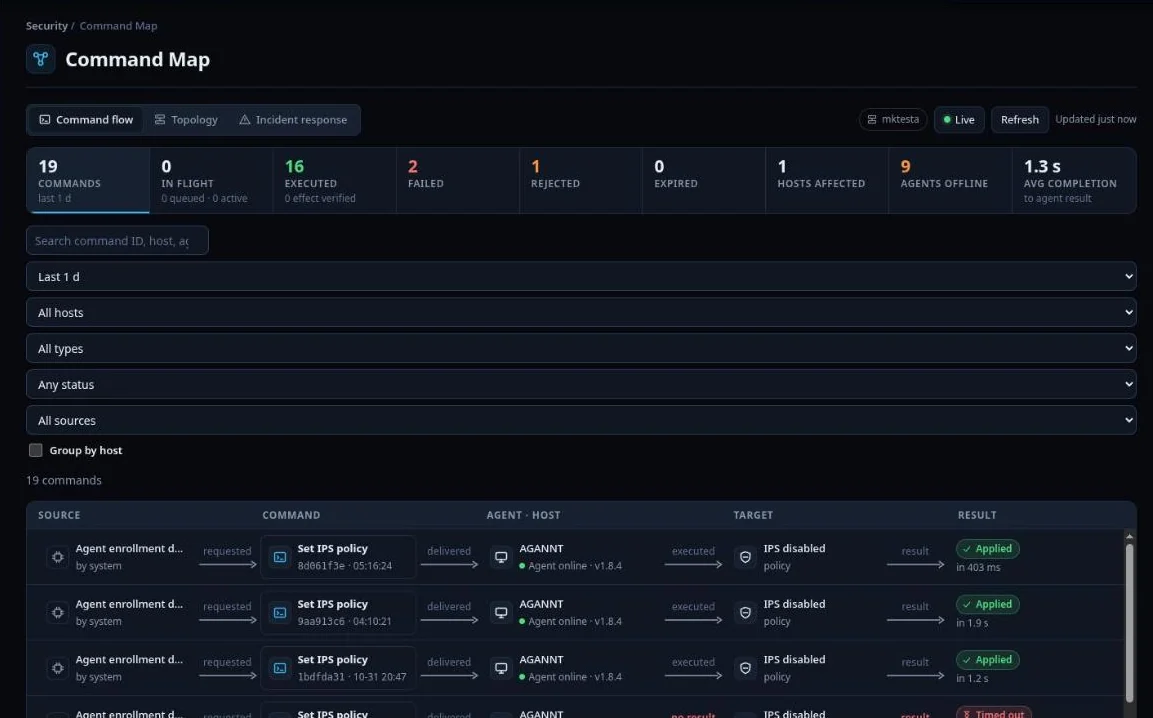
Every protective command, traced to its result.
Command Map follows each instruction from the platform to every agent and shows whether it was delivered, executed and applied. A live topology places each server by security state, from critical and uncontained to fully protected.
- Command flow from request to applied result
- Live topology by security state
- Failed and expired commands surfaced
- Incident response view
- Live updates, no refresh needed
OutcomeProof that every protective action actually reached its target.
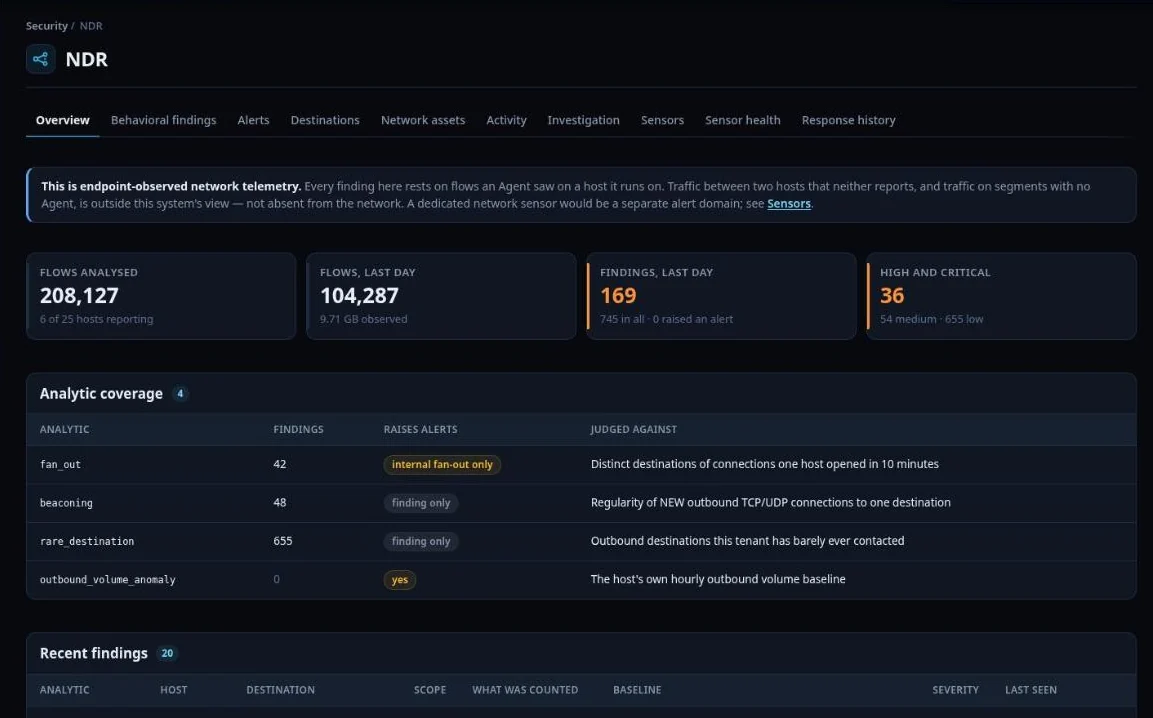
Network behavior that signatures miss.
NDR analyzes the connections your servers make and flags behavior that does not fit: hidden communication with attacker infrastructure, a server suddenly reaching many destinations, rare destinations and unusual volumes of data leaving the network.
- Beaconing detection
- Fan out detection
- Rare destination detection
- Outbound volume anomalies
- Findings mapped to MITRE ATT&CK
- Destination and network asset views
OutcomeBehavior based detection that complements signatures and catches what they cannot.
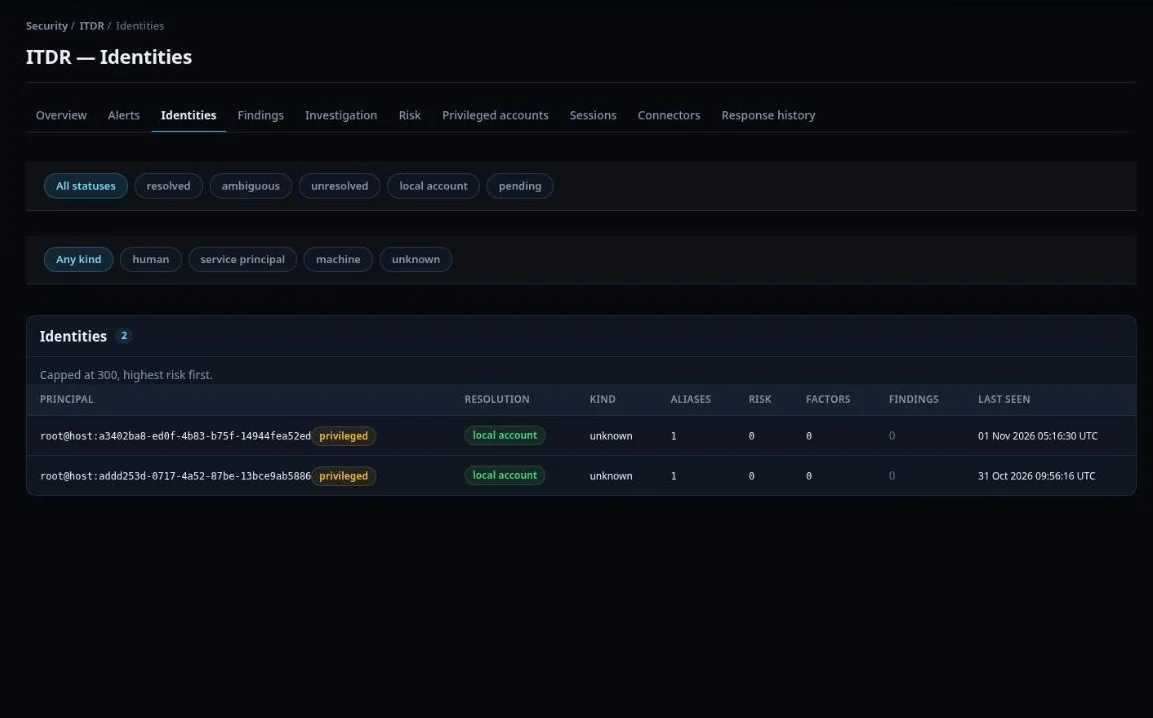
Protect the identities attackers target first.
ITDR brings accounts into the security picture. It resolves identities across servers, keeps privileged accounts under watch, tracks failed logins and sessions, and scores the risk of every identity so stolen or misused credentials do not go unnoticed.
- Identity resolution across servers
- Privileged account tracking
- Failed login and session monitoring
- Risk score for every identity
- Identity findings and investigation
- Connectors and response history
OutcomeAccount takeover and misuse become visible before they become a breach.
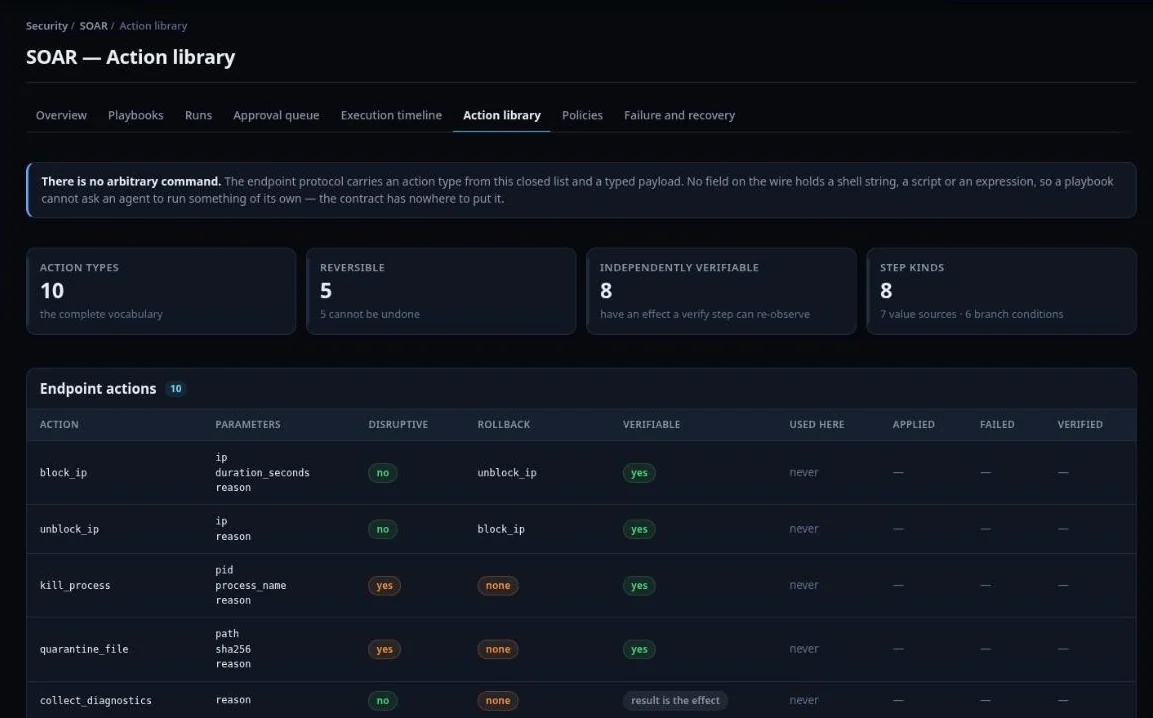
Automate response, without losing control.
SOAR turns response procedures into playbooks of typed steps, with approval gates where they matter and verification that every action actually took effect. Agents accept actions only from a closed, typed library, never an arbitrary command.
- Playbooks with approvals, delays and branches
- Closed library of typed actions
- Reversible actions where possible
- Verification that each action worked
- Approval queue and execution timeline
- Failure and recovery tracking
OutcomeConsistent, auditable response at machine speed, with people in charge.
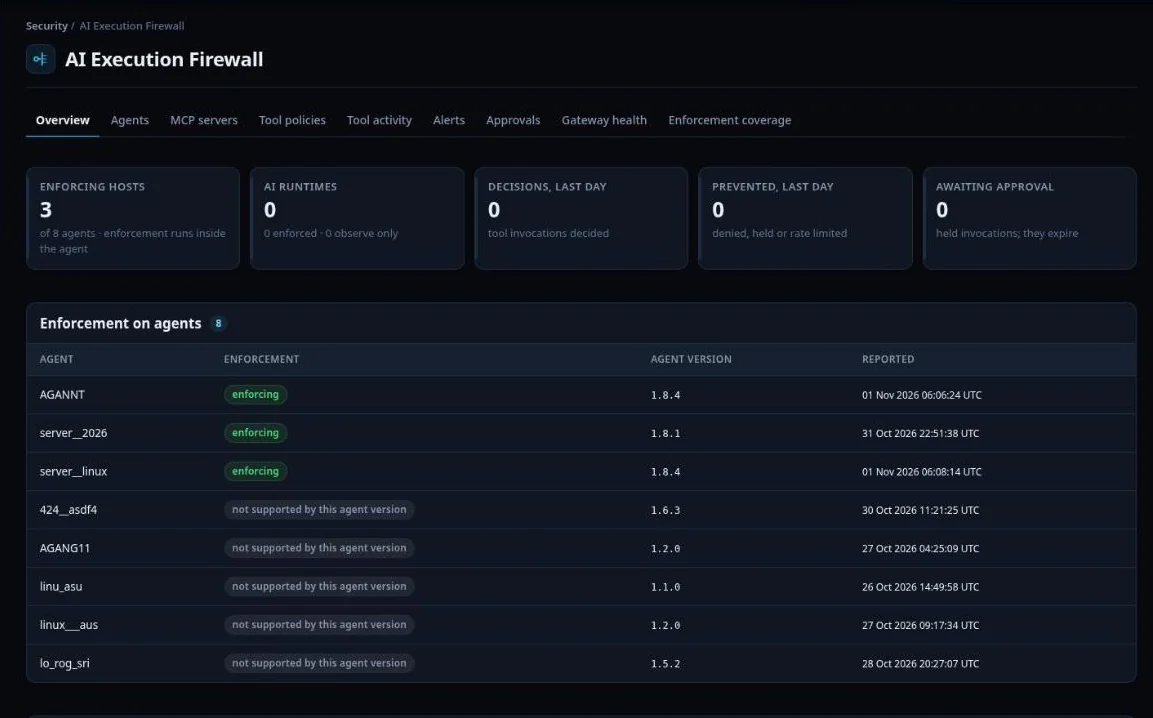
Guardrails for the AI agents on your servers.
As AI assistants and agents gain access to servers and tools, the AI Execution Firewall decides what they may run and enforces that decision inside the Armadillo agent on the host. Destructive or unknown tools are denied by default.
- Policies for each AI tool
- Deny by default for destructive and unknown tools
- Approval workflow for held actions
- Inventory of AI agents and MCP servers
- Tool activity and alerts
- Enforcement coverage per agent
OutcomeAdopt AI on your infrastructure without handing it the keys.
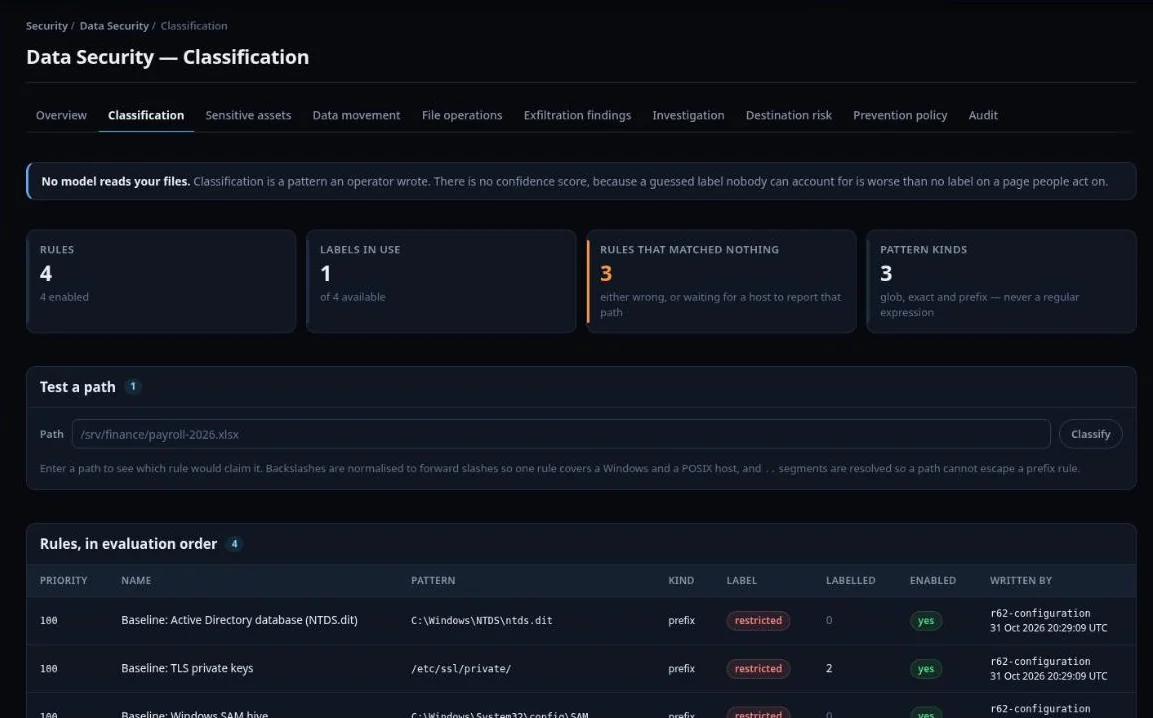
Know where sensitive data lives, and when it moves.
Data Security classifies sensitive files with rules your team writes and can test against any path, then flags access to classified files that is followed by an outbound transfer. No model guesses at your data: every label has a rule behind it.
- Restricted, confidential, internal and public labels
- Test any path against your rules
- Sensitive asset discovery
- Data movement and file operations
- Exfiltration findings
- Destination risk, prevention policy and audit
OutcomeSensitive data stays visible, governed and accounted for.
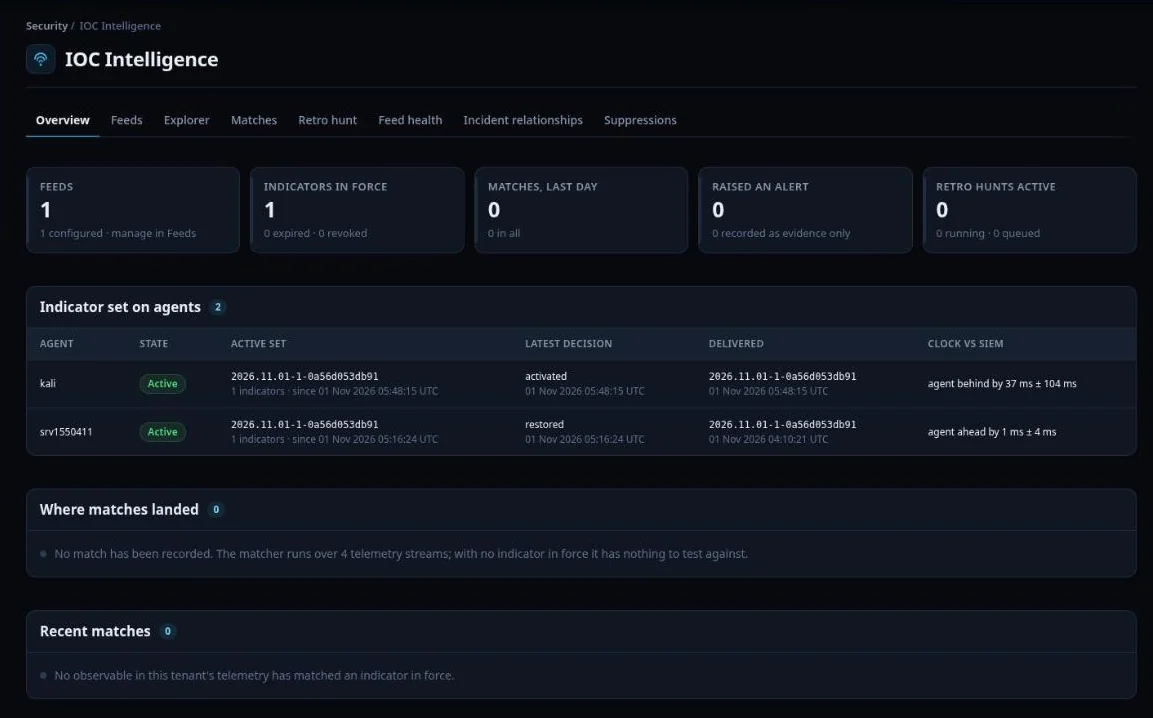
Global threat intelligence, at work on every server.
IOC Intelligence brings threat feeds into Armadillo, delivers the indicators to every agent and matches them against server activity, both live and looking back in time with retro hunts across stored telemetry.
- Feed management with reliability and expiry
- Indicators delivered to every agent
- Matching across server telemetry
- Retro hunts over historical data
- Feed health monitoring
- Suppressions and incident links
OutcomeKnown threats are recognized the moment they touch your environment.
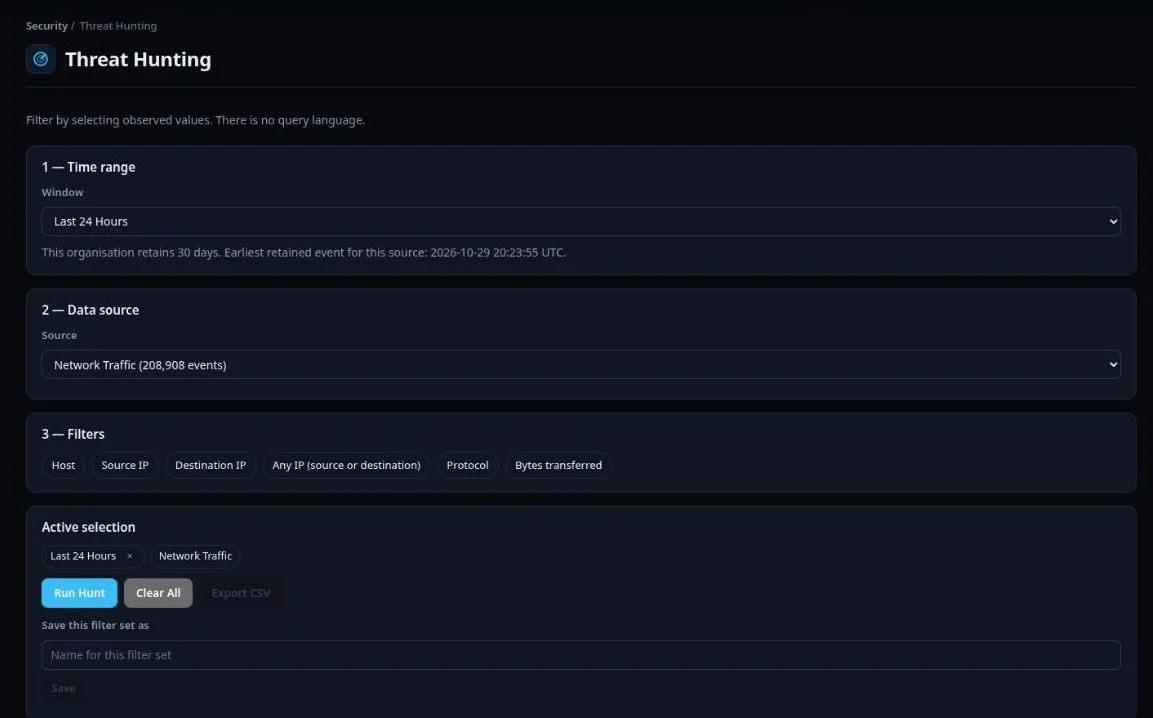
From a hunch to a closed case.
Analysts hunt across collected telemetry by selecting observed values, with no query language to learn. Related evidence is grouped into incidents, and cases track every investigation through to closure.
- Point and click threat hunting
- Saved searches and export
- Incidents built from correlated evidence
- Case management with linked alerts
- Alert archive with restore
- Email notifications
OutcomeInvestigations move faster, and nothing gets lost along the way.
- Firewalls
- Cloud audit logs
- Identity providers
- Other security tools

- Alerts linked to hosts
- Ticketing and chat
- Another SIEM
Bring your other security tools into one picture.
Armadillo takes in events from firewalls, cloud audit logs and identity providers, turns them into alerts with detection rules that are tested before activation, and links every external alert to the affected server.
- Firewall, cloud audit and sign in events
- Typed detection rules, tested before activation
- External alerts linked to affected servers
- Findings shared with ticketing, chat or another SIEM
OutcomeOne place to see and act on security events from across your environment.
Screens from the Armadillo console, test environment. See them on your own servers
06Data sovereignty06 / 07
Security analysis that stays in country
Armadillo is designed for deployment models where telemetry, logs and traffic are analyzed on site or on in country infrastructure, with rules that remain visible and auditable.
The deployment model is agreed with each customer. It supports data residency requirements; it does not by itself establish compliance with a specific regulation.

07Get started07 / 07
See Armadillo in your environment.
Three steps from first conversation to full protection.
- 1
Technical session
Your stack, your threat model, and how Armadillo would be deployed.
- 2
Pilot on your servers
A scoped evaluation in your own environment, with no obligation.
- 3
Rollout
Extend protection across your environment, at your pace.